By crawling through hundreds of Telegram channels, cybercriminal forums, and other open sources, 407 cyber operations against the space sector were identified in 2025, accounting for more than one attack per day.
The pattern was not random. Cyber activity surged alongside geopolitical crises, with notable spikes during tensions between Ukraine and the United States, the India-Pakistan crisis, and the Israel-Iran war.
Out of 407 identified operations, 183 distinct space-related entities in 46 countries were identified as targets, many of which were targeted repeatedly. The most targeted entities were Elbit Systems, Rafael, Antonov, NASA, Ukrkosmos, and Israel Aerospace Industries. Other identified targets include SpaceX, Airbus, Leonardo, Eutelsat, Gilat, ESA, GMV, etc.
Out of 407 identified cyber operations, 61% were distributed denial of service (DDoS), 13% were ransomware, 5% were data breaches, 4% were data leaks, 4% were data sales, 3% were unauthorized access, and 1% were either unauthorized access sale, malware, credential theft, website defacement, or vulnerability exploit.
More importantly, the perimeter of the threat is expanding. Attackers are increasingly targeting organizations that are not themselves space companies, but depend on space systems or sit somewhere in the space supply chain. For instance, an attack against the company GuraLP led to unauthorized access to GNSS receivers, affecting seismic monitoring in Italy. Similarly, an attack against the online conference tool Dooble Digital Solutions, which was used by a space company, and likely impacted its activities.
What is changing from previous years is the increasingly tangible operational consequences of cyberattacks against space systems. In South Africa, a ransomware attack against the national weather service disrupted its ability to connect its IT environment to weather stations for roughly a month. Even after services were partially restored, the organization continued operating at reduced capacity, forcing it to provide end-users with extrapolated data and lower-resolution imagery. Many users, including in the agricultural sector, were reportedly unaware of the disruption, despite its impact on the quality of the services they received. The incident also had financial consequences for the weather service itself. Similarly, a cyberattack affecting the satellite communications systems of two Iranian shipping companies disabled satcom modems across their fleets and enabled attackers to access company data, including each vessel’s satellite communication credentials.
Cyberattacks on the space ecosystem are no longer just about websites going offline. They are beginning to interfere with real-world services, operational continuity, and the systems on which entire sectors depend.
The Tip of the Iceberg
What we can see is not the space cyber threat landscape. It is the small part that breaks the surface.
Even defining what counts as a space cyberattack is difficult. Should every attack on Boeing qualify? What about an intrusion into NATO that exposes information about space agencies, or an attack on a company that depends on satellite data? Where the perimeter is drawn changes the picture.
The data is incomplete for another reason: many incidents are never disclosed. Researchers may identify hostile intent, offensive capabilities, academic demonstrations or claims by threat actors, yet still be unable to connect them to a confirmed operation. Access to primary sources is uneven, and tracking the same actors consistently over time is difficult, especially when cybercriminal forums and Telegram channels are regularly taken down, driving threat actors into closed spaces.
Public reporting adds another layer of distortion. Cybersecurity companies can only report what their sensors can see, and most of those sensors sit on terrestrial IT systems, not satellites. What ultimately gets published is then shaped by commercial incentives, customer and geopolitical alignment, and market demand. With few dedicated space cyber intelligence products and a fragmented global cyber threat intelligence (CTI) market, public visibility remains limited.
Even confirmed incidents rarely stand still. New disclosures can emerge months later and fundamentally change what we think happened, who was responsible, and how serious the impact really was. It was the case when the attack against Russian satellite communications company Dozor-Teleport disrupted connectivity for over 16 hours. Initially claimed by Wagner, the attack was later claimed by the Ukrainian Cyber Alliance.
The space cyber threat landscape is also clouded by noise. Threat actors often exaggerate or fabricate claims, while victims remain silent, leaving researchers to determine what is real with little evidence. Yet, even false claims matter as they signal interest in targeting the space sector.
Why Can’t We Identify Attacks Against a Satellite in Orbit Yet?
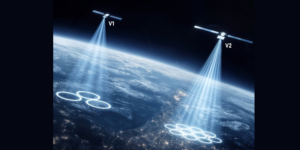
Of the 407 cyber operations identified in 2025, not a single one could be confirmed as targeting the space segment itself. That does not mean satellites are untouched. More likely, it means we are still blind to what happens on board.
We cannot reliably identify what we do not measure. On Earth, cybersecurity teams rely on sensors, logs and monitoring tools that record what happens inside a system. Those records allow analysts to reconstruct attacks, identify malicious behavior and improve future detection.
Satellites have not benefited from the same process. Most were not designed with dedicated cyber sensors, and many remain in orbit for years or decades, making upgrades difficult or impossible after launch. This creates a chicken-and-egg problem. To build effective detection systems, we need to know what an attack against a satellite looks like. But without sensors capable of observing such attacks, we lack the evidence needed to know what to detect.
Terrestrial cybersecurity overcame this problem gradually, through decades of accumulated incident data and gradual deployment of sensors over the internet and IT architectures. Space cybersecurity is trying to compress that learning curve into a much shorter period.
It means developing a new detection ecosystem tailored to spacecraft by using satellite telemetry to identify suspicious behavior, training systems to distinguish normal from abnormal activity, linking anomalies to space-specific threat frameworks like SPARTA or ESA SHIELD, and defining indicators that make sense for satellites rather than terrestrial IT.
That work is now underway. But until these capabilities become widespread, any public picture of cyber threats against the space segment will remain incomplete by design.
Closing the Space Cyber Threat Intelligence Gap
The space industry long relied on security-by-obscurity. Information was tightly controlled, software was proprietary, hardware was highly specialized, and systems were difficult for outsiders to access or understand.
That model is disappearing. Commercialization, the widespread use of commercial off-the-shelf components and big data have made space systems more accessible and more understandable.
The result is a form of insecurity by transparency. Threat actors should be assumed capable of finding the technical information they need to study, target, and potentially compromise space systems. Yet defenders still operate with limited space-specific cyber threat intelligence, weak information-sharing mechanisms, and little visibility into what happens on board satellites and within threat actors’ communities.
There is no realistic path back to obscurity. The only viable response is to make transparency work in favor of defenders by transitioning to security by transparency: developing space-specific threat intelligence, deploying on-board detection capabilities, and sharing information more systematically across the sector. If attackers can increasingly understand how space systems work, defenders need to become equally effective at understanding how those systems are being targeted.
Clémence Poirier is a Senior Cyber Defense Researcher at the Center for Security Studies (CSS) in Zurich, Switzerland. She is the author of the study “Space Cyber Threat Intelligence, Space Cyber Threat Landscape 2025.”